Foschini Group's UK arm TFG London hit by cyber incident at Phase Eight, Hobbs, Whistles
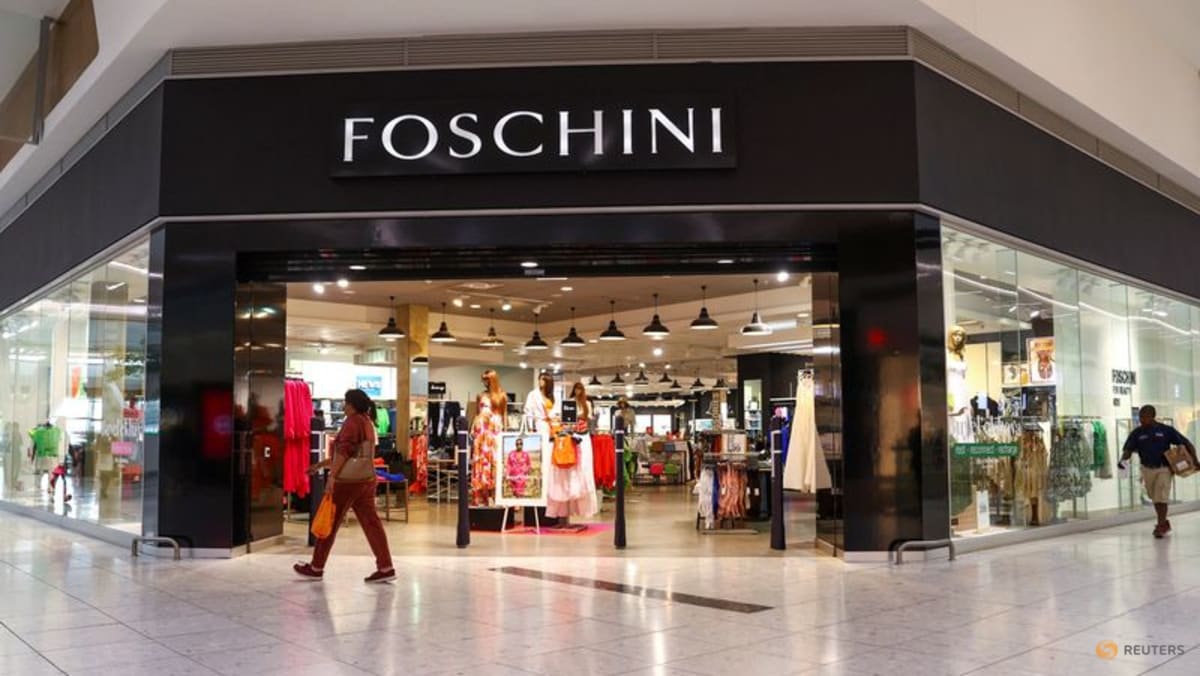
South Africa's The Foschini Group said its UK subsidiary TFG London detected a cybersecurity incident on Sunday 11 October that disrupted IT systems at Phase Eight, Hobbs and Whistles. Stores are trading; it is not yet known whether personal data was compromised.
Updated (version 2). New coverage since the last version from Daily Mirror.


1 / 3
The story, neutrally told
Centre · 1The Foschini Group (TFG), a South African fashion retailer, said on Tuesday 13 October that it was investigating a cybersecurity incident at its UK operations, TFG London, affecting its Phase Eight, Hobbs and Whistles brands. CNAN “said on Tuesday it was investigating a recent cybersecurity incident at its UK operations, affecting its Phase Eight, Hobbs and Whistles brands.” Read at CNA ↗ Centre · 2TFG London said it identified the incident on Sunday 11 October, and that it disrupted certain IT systems. Evening StandardN “On Sunday, 11 October, TFG London identified a cybersecurity incident affecting some of our IT systems” Read at Evening Standard ↗ CNAN “detected a cybersecurity incident over the weekend that disrupted certain IT systems” Read at CNA ↗ Centre · 2The company has engaged external cybersecurity specialists to contain the incident and has informed the relevant UK authorities. CNAN “TFG London has engaged external cybersecurity specialists to contain the incident and informed all relevant UK authorities” Read at CNA ↗ Evening StandardN “TFG said it had reported the incident to the relevant UK authorities.” Read at Evening Standard ↗
Centre · 2It has not established whether personal or other sensitive information was compromised; it said there is "no reason to believe that payment information is at risk" and would notify affected individuals or organisations if data is found to be compromised. Evening StandardN “Should the investigation establish that such information has been compromised, TFG London will notify affected individuals or organisations, as appropriate,” Read at Evening Standard ↗ CNAN “An investigation to establish whether any personal or other sensitive information has been compromised remains ongoing” Read at CNA ↗ Centre · 1Stores are open and trading as normal, but several IT systems remain unavailable and some website capabilities of the brands may not work while the investigation continues; the company apologised for the disruption. Evening StandardN “Stores are open as normal but some of our brand’s website capabilities may not be available as the investigation continues.” Read at Evening Standard ↗ Evening StandardN “although several of its IT systems remain unavailable.” Read at Evening Standard ↗ Mixed · 2TFG Africa and TFG Australia run on separate systems and are not affected, and the Daily Mirror reported that other UK brands such as Inside Story and White Stuff are also unaffected. Evening StandardN “TFG Africa and TFG Australia “run on separate systems and are not affected,” they added.” Read at Evening Standard ↗ Daily MirrorL “Other high street brands, including Inside Story and White Stuff, have not been affected.” Read at Daily Mirror ↗
Centre · 1The Evening Standard noted the incident came a week after Asos said an "unauthorised party" had accessed some customer personal data, with customers told that data storage firm Snowflake had been compromised; no link between the two incidents was reported. Evening StandardN “It comes a week after fast fashion business Asos said an “unauthorised party” had gained access to some personal data” Read at Evening Standard ↗ Evening StandardN “which claimed the data storage firm Snowflake had been compromised.” Read at Evening Standard ↗ Left · 1The Daily Mirror added that H&M was reported to be investigating claims it was targeted by a group called Shinyhunters, which previously claimed an attack on Jaguar Land Rover; it did not link that to the TFG London incident. Daily MirrorL “The Swedish fashion giant said it was looking into a potential cybersecurity incident made by a group called Shinyhunters, The Times reported.” Read at Daily Mirror ↗
Every sentence links to the reporting it rests on. The pill in front of each says where its sources sit: Left, Centre or Right when one side supplies at least half of them, Mixed when they are evenly split. The number is how many outlets it cites.
Left1 outlet
- Framing
- The Daily Mirror leads with the incident as the latest in a run of fashion-retail hacks, tying it to the ASOS breach in its headline and adding H&M and Shinyhunters context.
- Emphasis
- Pattern of attacks on fashion retailers, customer apology and payment-data reassurance.
- Leaves out or plays down
- Does not mention the unaffected TFG Africa and Australia operations or that several IT systems remain unavailable.
- Charged language
- “just days after ASOS hack”
- For example
-
“has been hit by a cyber attack - just days after ASOS was hacked” — Daily Mirror
Centre2 outlets
- Framing
- Short, factual reports built on the company statement; CNA gives a bullet-point summary from a business-news angle, while the Evening Standard adds UK consumer context and the Asos breach a week earlier.
- Emphasis
- Scope of affected brands and systems, containment steps, store trading and the unaffected African and Australian operations.
- Leaves out or plays down
- CNA omits the payment-information reassurance and the Asos comparison; neither outlet reports who is behind the incident or how it happened.
- For example
-
“while its operations in Africa and Australia are unaffected” — CNA
“The attack comes a week after fashion business Asos said an “unauthorised party” had gained access to some personal data” — Evening Standard
Right0 outlets
No right outlet in our sources has covered this story yet.
What every side reports
- TFG London detected a cybersecurity incident on the weekend of 11 October affecting Phase Eight, Hobbs and Whistles.
- External cybersecurity specialists have been engaged and UK authorities informed.
- TFG Africa and TFG Australia are unaffected.
- The company has no reason to believe payment information is at risk, and whether other data was compromised is still under investigation.
-
The incident disrupted IT systems at TFG's UK operations, affecting Phase Eight, Hobbs and Whistles.
Reported- Reports 3
- Daily Mirror, CNA, Evening Standard
-
External cybersecurity specialists are working on the investigation and containment of the incident.
Reported- Reports 3
- Daily Mirror, CNA, Evening Standard
The Foschini Group organisation
Says it detected the incident, is investigating with external specialists, has informed UK authorities, sees no reason to believe payment information is at risk, and says its African and Australian operations are unaffected.
“its operations in Africa and Australia are unaffected” — CNA
“no reason to believe that payment information is at risk” — Evening Standard
Left1 article
-
Phase Eight, Hobbs and Whistles owner TFG London hit by cyber attack - just days after ASOS hack
Mixed Consumer-focused report that places the incident within a wave of retail hacks (ASOS, H&M), while relaying the company's reassurances.
Centre3 articles
-
CNAN ·
South African fashion retailer Foschini Group's UK arm hit by cyber incident
Neutral Concise bullet summary of the company statement, focused on investigation and unaffected regions.
-
Hobbs and Whistles owner struck by cyber attack
Neutral Consumer-focused report stressing the apology, payment-data reassurance and the Asos hack a week earlier.
-
TFG London: Cyberattack hits UK fashion brands Hobbs, Whistles and Phase Eight
Neutral Factual report of systems knocked out, unknown data exposure and unaffected TFG divisions, with Asos context.
Right0 articles
No coverage yet.
- 13 Oct 06:37 First CNAN South African fashion retailer Foschini Group's UK arm hit by cyber incident
- 13 Oct 07:37 +1h Evening StandardN Hobbs and Whistles owner struck by cyber attack
- 13 Oct 07:39 +1h 2m Evening StandardN TFG London: Cyberattack hits UK fashion brands Hobbs, Whistles and Phase Eight
- 13 Oct 08:32 +1h 55m Daily MirrorL Phase Eight, Hobbs and Whistles owner TFG London hit by cyber attack - just days after ASOS hack
Times are when each article was published, or when we first saw it if the outlet gave no time.
Ask about this story
Loading…