Pentagon personnel database breach exposes data on nearly 3 million people
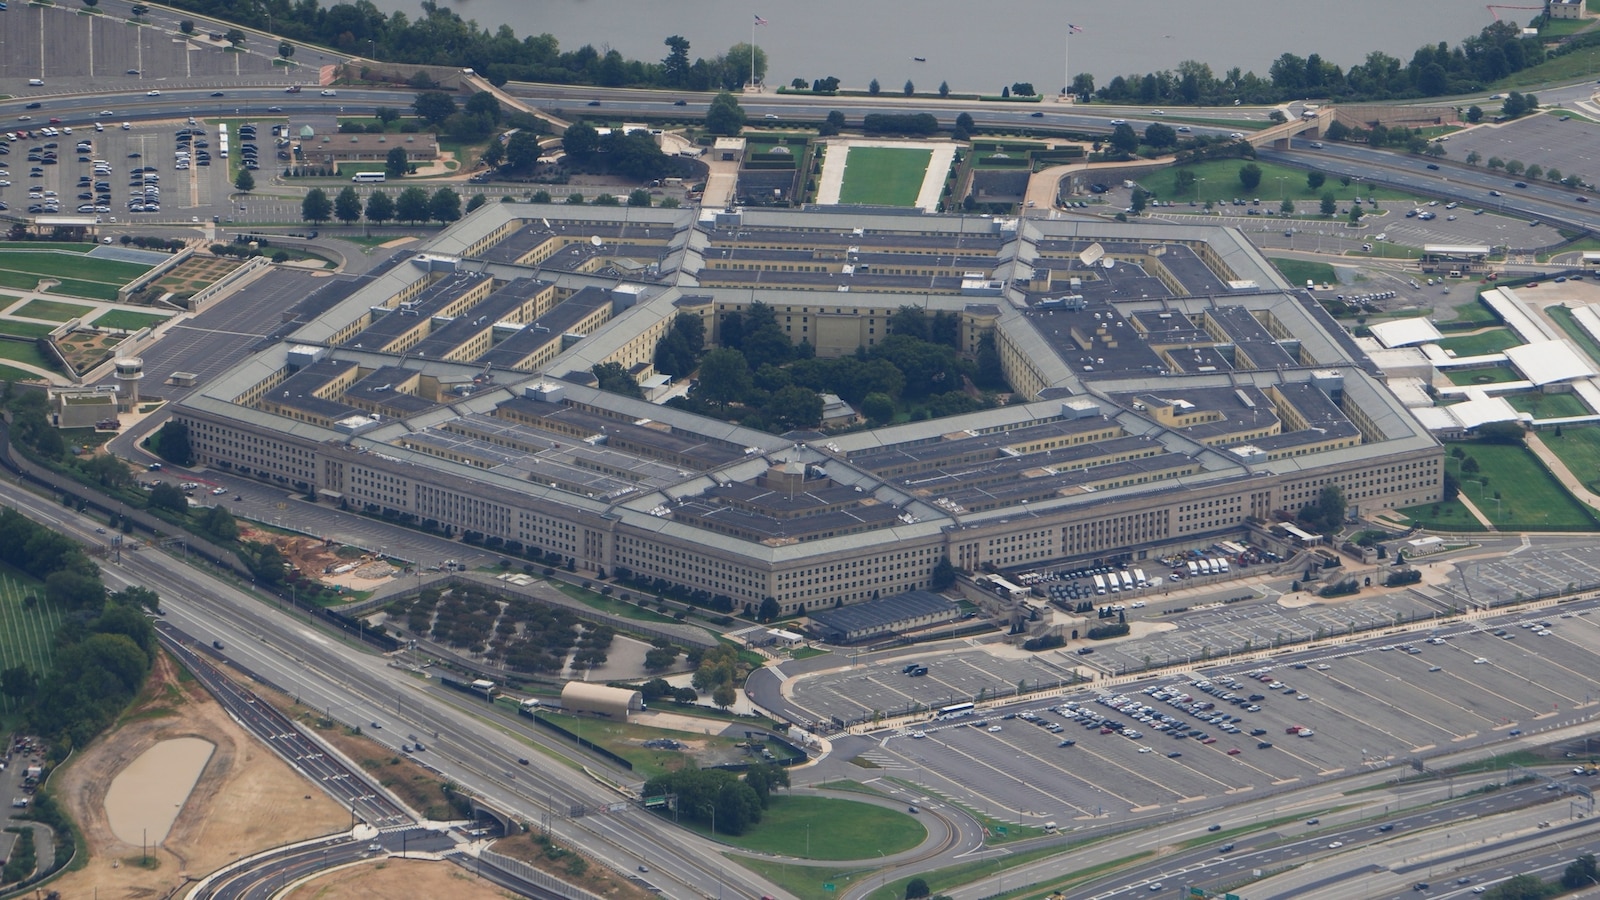
A Defense Manpower Data Center system was accessed without authorisation between October 2025 and July 2026, exposing Social Security numbers and other records of about 2.8 million living people and nearly 300,000 deceased people, a Pentagon official said.

1 / 3
The story, neutrally told
A Pentagon personnel system run by the Defense Manpower Data Center (DMDC) was accessed without authorisation, exposing sensitive records of military and civilian personnel. ABC NewsLC “A breach of the Pentagon’s sprawling personnel database exposed sensitive information belonging to a massive swath of military personnel” Read at ABC News ↗ TechCrunchN “several unauthorized users exploited a security vulnerability in an unspecified file-sharing system” Read at TechCrunch ↗ A defense official told ABC News the breach affected 2.76 million living people and another 294,000 who are deceased; TechCrunch, citing CNN and Federal News Network, put the figures at about 2.8 million and close to 300,000. ABC NewsLC “The breach affected 2.76 million living people and another 294,000 who are deceased, the official said.” Read at ABC News ↗ TechCrunchN “the breach affects about 2.8 million living people, and close to 300,000 people who are deceased” Read at TechCrunch ↗ The unauthorised access ran from October 2025 to July 2026, when DMDC said it discovered and fixed the vulnerability. ABC NewsLC “between October 2025 and July 2026. Upon discovery, DMDC immediately remediated the vulnerability” Read at ABC News ↗ TechCrunchN “between October 2025 and mid-July 2026” Read at TechCrunch ↗
The exposed data included Social Security numbers and details of jobs held; a notification shared on Reddit, described by TechCrunch, also lists names, dates of birth, sex and race, and says the records were unencrypted. ABC NewsLC “including Social Security numbers and details about the jobs they held” Read at ABC News ↗ TechCrunchN “The notice says that the personnel records were unencrypted.” Read at TechCrunch ↗ Defense officials said they have found no evidence the data has been misused; ABC reports they are offering identity protection and credit monitoring, while TechCrunch notes the department did not say how it reached that conclusion. ABC NewsLC “are offering identity protection and credit monitoring resources” Read at ABC News ↗ TechCrunchN “but did not say how it reached that conclusion” Read at TechCrunch ↗ DMDC holds more than 60 million records on troops, civilians, contractors, retirees and family members, and manages identity credentials for access to Pentagon systems and bases. ABC NewsLC “The agency maintains more than 60 million personnel records.” Read at ABC News ↗ TechCrunchN “leading identity management provider” Read at TechCrunch ↗
Both outlets place the breach alongside a recent FBI breach attributed to the ShinyHunters group, which has said it will not release the stolen data; the identities of the Pentagon hackers are not known. ABC NewsLC “the hacking group shinyhunters claimed it won't release the data as it previously said it would” Read at ABC News ↗ TechCrunchN “whose identities are not known” Read at TechCrunch ↗ TechCrunch compares the incident with the 2015 Office of Personnel Management breach, broadly attributed to China, which affected more than 22 million government employees. TechCrunchN “more than 22 million U.S. government employees” Read at TechCrunch ↗
Every sentence links to the reporting it rests on.
Left1 outlet
- Framing
- Leads with national-security implications and the scale of exposure, sourced to a defense official, then links to the FBI jobs-portal breach.
- Emphasis
- Exact figures, job details in files, official statement, FBI employee guidance.
- Leaves out or plays down
- Does not mention the records were unencrypted or the 2015 OPM comparison.
- Charged language
- “sprawling personnel database”“massive swath”
- For example
-
“The scope and sensitivity of the exposed information could raise national security concerns” — ABC News
Centre1 outlet
- Framing
- Frames it as theft by hackers in a months-long breach, part of a spate of federal-worker data thefts, with security-editor context.
- Emphasis
- Unencrypted records, unverified no-misuse claim, DMDC's role, historical OPM comparison.
- Leaves out or plays down
- Gives rounded figures and does not report the FBI employee guidance on media contact.
- Charged language
- “counterintelligence disaster”“Hackers stole”
- For example
-
“the latest in a spate of thefts involving federal workers’ data in recent months” — TechCrunch
Right2 outlets
No right outlet in our sources has covered this story yet.
What every side reports
- DMDC systems were accessed by unauthorised users between October 2025 and July 2026.
- About 2.8 million living and roughly 300,000 deceased people were affected.
- Social Security numbers were exposed.
- Officials say there is no evidence of misuse.
- The breach follows an FBI breach linked to ShinyHunters.
Where accounts differ
-
Exact number of people affected
- Left
- ABC News: 2.76 million living and 294,000 deceased, per a defense official.
- Centre
- TechCrunch: about 2.8 million living and close to 300,000 deceased, citing CNN and Federal News Network.
Pentagon organisation
Through DMDC and unnamed officials, it says a small number of unauthorised users accessed the system, the flaw was fixed on discovery, and there is no indication of misuse.
“by a small number of unauthorized users between October 2025 and July 2026” — ABC News
“does not have any indication that the information was misused” — TechCrunch
Left1 article
-
Pentagon breach exposed sensitive data on nearly 3 million people
Neutral Official-sourced news report stressing scale, sensitivity and the parallel FBI breach.
Centre1 article
-
Hackers stole millions of US military personnel records during months-long data breach
Critical Tech-security report describing theft of records, noting lack of encryption and unexplained no-misuse claim.
- 29 Sep 01:39 First ABC NewsLC Pentagon breach exposed sensitive data on nearly 3 million people
- 30 Sep 20:29 +42h 50m TechCrunchN Hackers stole millions of US military personnel records during months-long data breach
- 30 Sep 22:31 +44h 52m Fox NewsR Pentagon data breach exposes Social Security numbers, personal info of 2.76M US military, civilian personnel
- 30 Sep 23:16 +45h 36m Just the NewsRC Pentagon data breach exposes info of more than 2.7 million US military and civilian personnel
Times are when each article was published, or when we first saw it if the outlet gave no time.